
Summary:
Recently the Switch 2 scene saw a fast-moving jailbreak named ns2jb that gave researchers access to the console’s filesystem and allowed asset extraction from several titles. Reports show RomFS and other game files for Deltarune Chapters 1-4, a beta datamine of The Duskbloods, and model assets from Mario Kart World have circulated within modding and datamining communities. These dumps appear to be asset-level extractions rather than complete, emulator-ready game images, and the exploit is tethered to firmware 23.0.1. Nintendo has already taken visible steps, including removing the entry-point title from the eShop, while developers test alternate entry points and extraction tools. This story matters for modders, archivists, and players because it highlights the tension between research, preservation, and piracy risk, and it will shape how the community and Nintendo respond in the coming days and weeks.
What happened wtih ns2jb a quick recap of the reports and timeline
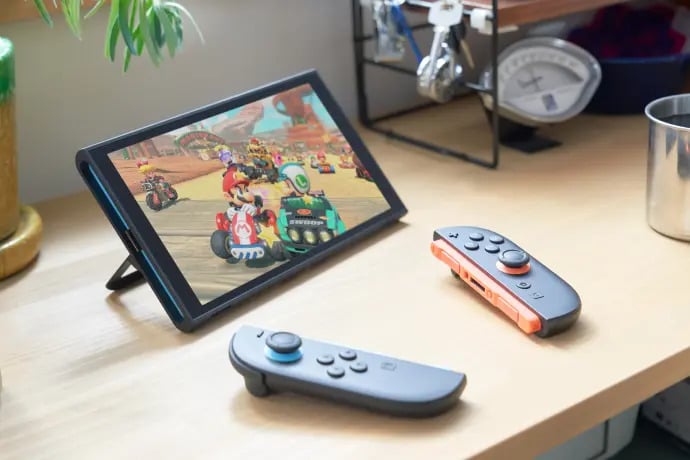
The last few days brought rapid developments around a software-only jailbreak called ns2jb. Researchers publicly demonstrated the exploit on real Switch 2 hardware and then used it to read game files from the console’s filesystem. Community posts and news outlets showed extracted assets – a 3D Peach model from Mario Kart World, datamines of a FromSoftware beta known as The Duskbloods, and files tied to Deltarune Chapters 1-4. The exploit was tied to firmware 23.0.1 and used an entry point in a now-delisted title. Because the situation unfolded so quickly, claims and counterclaims are still being checked, but the basic timeline – exploit released, files extracted, community datamining and Nintendo removing the entry app – is supported by multiple independent reports.
The ns2jb exploit explained and what “tethered” means
ns2jb is a userland, software-only exploit that targets the filesystem sysmodule on Switch 2 units running firmware 23.0.1. In practice that means it allows native code execution with the privileges of that sysmodule but it does not provide kernel-level control or access to the hardware encryption keys. Tethered means the jailbreak does not persist across reboots – you have to run the exploit again every time the console restarts. That limits practical risks for casual users but still gives researchers a window to dump files, test patches, and run homebrew in a single session. The exploit’s constraints explain why asset dumps are possible while full, installable ROM images remain out of reach for now.
What was actually dumped – assets, RomFS and datamines, not full ROM images
Multiple reports point to RomFS extractions and asset-level dumps rather than complete, decrypted game images. In community posts and screenshots, Deltarune’s first four chapters were shown as extracted files and differential patches, The Duskbloods beta appeared in a datamine screenshot, and Mario Kart World had model and texture files pulled for inspection and modding. Those results are valuable – assets let modders and dataminers examine game models, music and textures – but they are not the same as a full ROM you can install and run on a PC emulator. The current public evidence shows readable game files in places, while other parts remain encrypted or incomplete.
Why these dumps do not equal instant emulation or a piracy pipeline
It’s tempting to see any dump headline and assume an emulator will appear overnight, but several technical and legal barriers remain. The reported exploit does not extract the console’s encryption keys and does not grant kernel execution, both of which are normally required to produce installable images that run outside the original hardware. Emulators need detailed firmware and hardware knowledge to faithfully reproduce the system environment, and even a full firmware dump does not automatically translate to a working PC build. That gap matters – researchers can study assets and system modules, but turning them into runnable ROMs or a widely usable emulator requires additional breakthroughs that have not been publicly demonstrated.
Nintendo’s response so far and likely next steps
Nintendo has already taken visible action by removing the title used as an entry point from the eShop registry, a step meant to limit casual exploitation. Beyond that, public reporting suggests Nintendo has been in contact with some community developers, and a security patch for affected firmware versions is likely on the way. Removing an app is a fast first move, but patches and legal measures tend to follow. For Switch 2 owners who care about homebrew or hacking, this likely means the window for any tethered exploit will be short-lived unless researchers find alternate entry points that rely on different software or components.
What this means for homebrew, modding, and datamining communities
For modders and homebrew fans the story is a mixed bag. On one hand, having access to game assets and some system modules lets talented hobbyists create mods, custom models, and preservation work faster than before. Examples of early mods and model swaps circulated within days, showing how quickly creative work can follow an exploit. On the other hand, the tethered nature and firmware dependence mean this is early-stage research rather than a stable platform. Responsible members of the community often treat these dumps as a research opportunity – to document, archive, and build tools – while avoiding actions that enable piracy or break the rules of online services.
Risks for players, legal and ethical considerations to keep in mind
If you own a Switch 2, the immediate advice from many community sources is to avoid running untrusted code, keep your console offline if you care about remaining on a vulnerable firmware version, and be cautious about downloading files from unofficial sources. There are real legal and safety risks tied to hosting and sharing protected game files. Beyond potential copyright issues, poorly built exploits and tools can brick consoles or expose private data. Respecting developers and publishers while preserving game history is a hard balance, and many in the scene emphasize that datamining for research and archiving often sits in a different ethical space than posting full, installable ROMs online.
How NintendoReporters will follow this story and where to find more
NintendoReporters will keep tracking confirmed developments and community responses as the situation evolves, and we’ll focus on verified milestones rather than rumor. If you want ongoing coverage of the Switch 2 ecosystem, our Nintendo Switch 2 hub and our Nintendo News section collect updates and analysis as they arrive. We also have editorial context about the history and ethics of homebrew and emulation that readers may find useful – see our piece on homebrew, emulation and piracy. We encourage readers to share tips and screenshots via our contact page if they have verifiable details to contribute.
Conclusion
The ns2jb reports show the Switch 2 research scene moving fast – assets and parts of games have been extracted and shared, but the technical reality still limits what those dumps enable today. This matters for modders, archivists and players because it changes what can be inspected and preserved, while also raising clear risks around piracy and device stability. Expect more patches, more testing by community researchers, and ongoing discussion about ethics and legality. NintendoReporters will continue to monitor confirmed reporting and community developments, and we’ll bring updates as they are verified.
FAQs
- Can I run Switch 2 games on my PC now?
- No – current dumps are asset-level and the exploit does not provide encryption keys or kernel execution needed to make installable ROM images that run on public emulators.
- Which games were reported as dumped?
- Community reports and screenshots show extractions tied to Deltarune Chapters 1-4, a beta datamine of The Duskbloods, and asset pulls from Mario Kart World, but these are primarily RomFS and model/textures assets rather than full decrypted ROMs.
- Is the exploit permanent or safe to use?
- The exploit is tethered and only works on firmware 23.0.1; it does not persist through a reboot and can brick consoles if used incorrectly. Exercise caution and follow trusted developer guidance if you experiment.
- Has Nintendo done anything about this yet?
- Yes – Nintendo removed the entry-point app from the eShop immediately after reports surfaced, and further firmware patches or actions are likely to follow.
- Where can I get trustworthy updates?
- Follow established outlets and community hubs rather than raw social posts; our Nintendo News pages and the Switch 2 hub are good starting points, and we will continue to verify and report confirmed changes.
Sources
- Nintendo Switch 2 hackers begin dumping Mario Kart World and other games following jailbreak, VideoCardz, October 25, 2026
- Switch 2 jailbreak produces 1st game dumps even as Nintendo responds to piracy threat, Notebookcheck, October 24, 2026
- What is ns2jb? The Switch 2 jailbreak situation explained, GBAtemp, October 24, 2026
- Switch 2 Firmware Dump: 23.0.1 Exploit, No Emulator [2026], Tech Insider, October 25, 2026